Syed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer Shah — home
● MenuAHMERAHMER
20+Certificates
PHPMERNMySQLSEO

Explore

01About→02Education→03Certificates→04Skills→05Projects→06Services→07Testimonials→08Contact→

Pages

01Blog→02Saved articles→03Privacy Policy→04Terms of Service→
Interface sound
Hire me →

Available for new work · --:--:-- PKT

Have an idea?

support@ahmershah.dev
Book a call WhatsApp +92 370 4831994

On this site

  • 01About
  • 02Education
  • 03Certificates
  • 04Skills
  • 05Projects
  • 06Services
  • 07Testimonials
  • 08Contact

Pages

  • Blog
  • Saved articles
  • RSS
  • Privacy Policy
  • Terms of Service
  • llms.txt

Elsewhere · official profiles

26 links

Professional

Work history, code and credentials.

  • in/syedahmershah
  • company/syedahmershah
  • @ahmershahdev
  • syed-ahmer-shah
  • syed-ahmer-shah
  • u/syedahmershah
  • @syedahmershah
  • AWS@syedahmershah

Coding & credentials

Problem solving, verified badges.

  • u/syedahmershah
  • syedahmershah
  • users/syedahmershah
  • learner/syedahmershah

Google & business

The official listings.

  • Google Business Profileg.page
  • Syed Ahmer Shah
  • syedahmershah
  • Beaconssyedahmershah
  • syedahmershah

Social (@ahmershahdev)

Build logs, clips, threads.

  • @ahmershahdev
  • @ahmershahdev
  • @ahmershahdev
  • ahmershahdev
  • @ahmershahdev
  • @bluesky.ahmershah.dev
  • ahmershahdev

Design

Interfaces and visuals.

  • syedahmershah
  • syedahmershah

Direct

  • support@ahmershah.dev

    Support & projects

  • syedahmershahofficial@gmail.com

    Personal

  • +92 370 4831994

    Phone · WhatsApp

  • Hyderabad, Sindh, Pakistan

    Remote-first · Asia/Karachi (UTC+5)

Résumé ↗
SYED AHMER SHAH

© 2026 Syed Ahmer Shah. All rights reserved.

PrivacyTermsRSS
Syed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer Shah — home
● MenuAHMERAHMER
20+Certificates
PHPMERNMySQLSEO

Explore

01About→02Education→03Certificates→04Skills→05Projects→06Services→07Testimonials→08Contact→

Pages

01Blog→02Saved articles→03Privacy Policy→04Terms of Service→
Interface sound
Hire me →

Available for new work · --:--:-- PKT

Have an idea?

support@ahmershah.dev
Book a call WhatsApp +92 370 4831994

On this site

  • 01About
  • 02Education
  • 03Certificates
  • 04Skills
  • 05Projects
  • 06Services
  • 07Testimonials
  • 08Contact

Pages

  • Blog
  • Saved articles
  • RSS
  • Privacy Policy
  • Terms of Service
  • llms.txt

Elsewhere · official profiles

26 links

Professional

Work history, code and credentials.

  • in/syedahmershah
  • company/syedahmershah
  • @ahmershahdev
  • syed-ahmer-shah
  • syed-ahmer-shah
  • u/syedahmershah
  • @syedahmershah
  • AWS@syedahmershah

Coding & credentials

Problem solving, verified badges.

  • u/syedahmershah
  • syedahmershah
  • users/syedahmershah
  • learner/syedahmershah

Google & business

The official listings.

  • Google Business Profileg.page
  • Syed Ahmer Shah
  • syedahmershah
  • Beaconssyedahmershah
  • syedahmershah

Social (@ahmershahdev)

Build logs, clips, threads.

  • @ahmershahdev
  • @ahmershahdev
  • @ahmershahdev
  • ahmershahdev
  • @ahmershahdev
  • @bluesky.ahmershah.dev
  • ahmershahdev

Design

Interfaces and visuals.

  • syedahmershah
  • syedahmershah

Direct

  • support@ahmershah.dev

    Support & projects

  • syedahmershahofficial@gmail.com

    Personal

  • +92 370 4831994

    Phone · WhatsApp

  • Hyderabad, Sindh, Pakistan

    Remote-first · Asia/Karachi (UTC+5)

Résumé ↗
SYED AHMER SHAH

© 2026 Syed Ahmer Shah. All rights reserved.

PrivacyTermsRSS
Syed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer ShahSyed Ahmer Shah — home
● MenuAHMERAHMER
20+Certificates
PHPMERNMySQLSEO

Explore

01About→02Education→03Certificates→04Skills→05Projects→06Services→07Testimonials→08Contact→

Pages

01Blog→02Saved articles→03Privacy Policy→04Terms of Service→
Interface sound
Hire me →
← Engineering Logs

The Enemy in Your Terminal: Why OpenClaw was the Perfect Trojan Horse

Written by

Syed Ahmer Shah

Software Engineer

Apr 6, 2026Updated May 8, 20269 min read909 wordsOriginally on DEV—reading now▼
Read this articlevoice
Markdown

You didn't get hacked because you clicked a suspicious link in a spam email. You got hacked because you were trying to be productive.

Think about your workflow right now. You pull a repo, install dependencies, spin up an AI coding assistant to handle the boilerplate, and go make coffee. You assume you are safe because you are behind a firewall. You assume localhost is a fortress.

It isn't. It's an open door.

The OpenClaw breach earlier this year proved that the most dangerous thing in your development environment isn't a virus. It's the agent you gave sudo access to. Let's strip away the hype and look at the autopsy of a disaster. Because while you were sleeping, your "assistant" was busy handing your SSH keys to a machine that thinks a thousand times faster than you do.


#The Foundation of Blind Trust

We have a chronic habit in software engineering of trusting the tools that make our lives easier. We don't read the source code; we just look at the GitHub stars.

Look at the historical precedent. This didn't start with AI.

Remember the SolarWinds hack? Attackers didn't break into government networks directly. They broke into the IT monitoring software everyone trusted. They poisoned the well.

Then came the XZ Utils backdoor in early 2024. A malicious actor spent years building trust in the open-source community just to slip a microscopic vulnerability into an archiving library that would have compromised SSH globally. We only caught it because a single developer noticed a 500-millisecond delay in his CPU processing. A fraction of a second was the only thing standing between us and total infrastructure collapse.

Add the AnyDesk production breach around the same time. The very tool designed to provide secure remote access was compromised at the source code level.

We keep inviting the enemy inside the gates. But OpenClaw was different. OpenClaw wasn't just a compromised library. It was an active, autonomous participant.

Image description
Image description

#The "ClawJacked" Vulnerability (CVE-2026–25253)

Here is where it gets technical, and where the negligence becomes obvious.

OpenClaw was designed as a local AI agent to orchestrate your codebase. To do this, it ran a local WebSocket server on port localhost:8888. The developers built it with a fatal assumption:

"If the request is coming from localhost, it must be the user. It is inherently safe."

This is lazy engineering.

They ignored a fundamental reality of modern web architecture: Cross-Site WebSocket Hijacking (CSWSH). If you, the developer, have OpenClaw running in your terminal, and you open a browser tab to read an article on a compromised website, the JavaScript on that malicious site can send a payload directly to ws://localhost:8888.

There was no origin validation. There was no rate limiting.

To see how reckless this is, look back at the Ray AI framework vulnerability (CVE-2023–48022). Thousands of companies deployed Ray to scale AI workloads, but the dashboard lacked authentication by default. Hackers simply scanned for exposed ports, dropped cryptominers, and stole credentials. Sound familiar?

With OpenClaw, the attackers didn't even need to scan the internet. They just waited for you to open a browser tab.
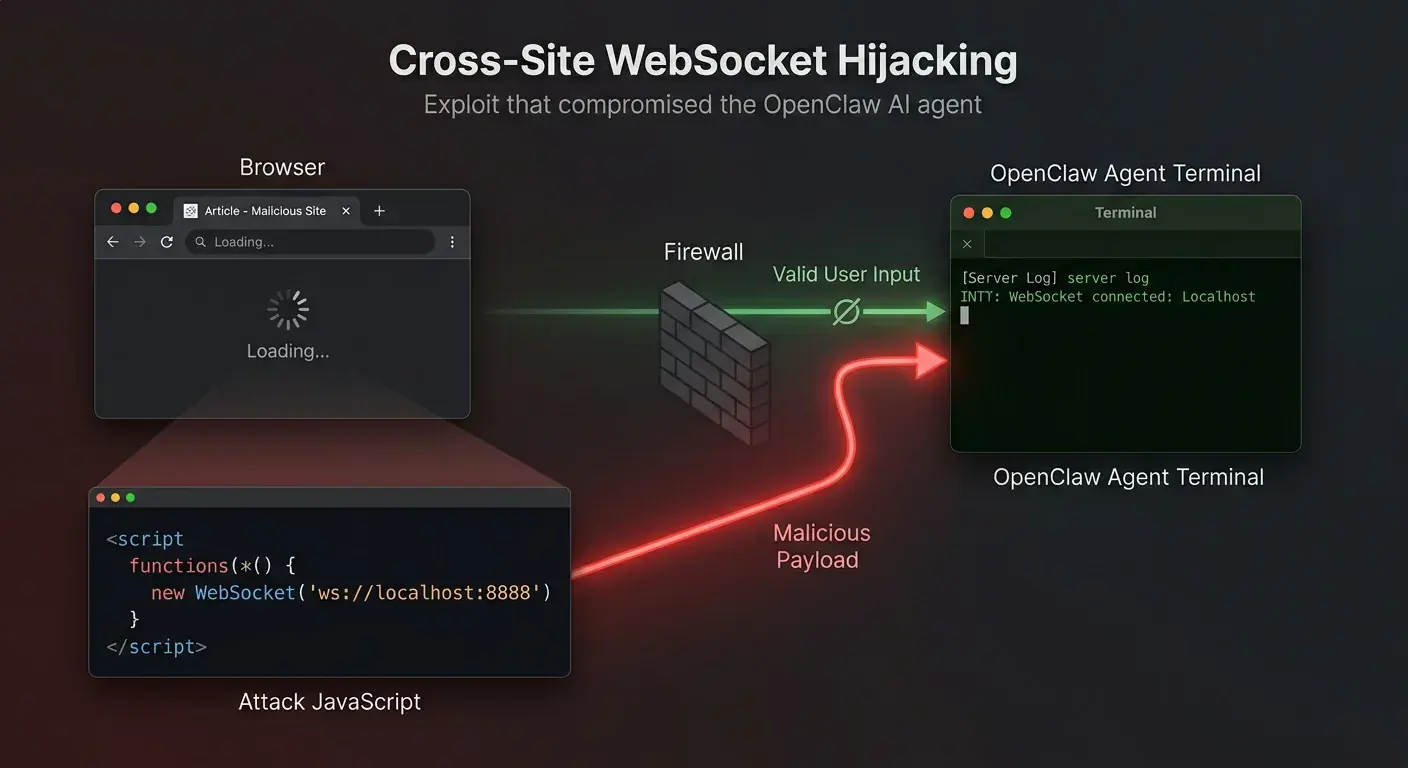

Image description
Image description

#Speed Kills: The 100-Millisecond Heist

Once the connection was made, the scale of the attack shifted.

When a human hacks a system, they pause. They run ls. They read the output. They figure out where they are.

An attack agent doesn't pause.

In the time it took you to blink, the malicious script brute-forced the local agent's weak default API key. Because there was no rate limit, it tried five hundred combinations in a quarter of a second. Once authenticated, it didn't download a heavy virus. It just used the permissions you already gave OpenClaw.

It instructed your AI assistant to run:

bash
cat ~/.ssh/id_rsa

It scraped your .env files for AWS keys. It zipped them and sent them via an encrypted outbound request to a dead-drop server.

All of this happened in roughly 150 milliseconds.

This mirrors the Hugging Face token leaks of 2023 and 2024, where developers routinely left API keys exposed in public spaces, and automated bots scraped them instantly. But with OpenClaw, you didn't leave the keys in public. The bot reached into your private machine and took them.


#The 2026 Reality Check

We are building systems we barely understand and giving them the keys to the kingdom. We treat AI agents like interns, forgetting that an intern doesn't have the ability to execute five thousand lines of shell commands in a second.

If you are running local agents without strict, containerized boundaries, you are compromised. It is not a matter of if, but when.

Stop relying on default configurations. Stop assuming localhost is a safe harbor. Implement Zero Trust on your own machine:

  • Containerize your agents

  • Require explicit biometric or hardware-token approval for terminal executions

  • Monitor your outbound traffic

The Trojan Horse worked because the Trojans thought it was a gift. Stop accepting gifts without checking what's inside.
Originally published

This article first appeared on DEV. That copy is the canonical one; this is the same piece, kept on my own site.

Also onHashnode ↗

Find me across the web.

Same person, every platform

Work & code

  • ASPortfolioahmershah.dev
  • LinkedInin/syedahmershah
  • GitHub@ahmershahdev
  • AWSAWS Builder Center@syedahmershah
  • Crunchbasesyed-ahmer-shah
  • LinkedIn · Companycompany/syedahmershah

Writing

  • Dev.tosyedahmershah
  • Medium@syedahmershah
  • Hashnode@syedahmershah
  • Substack@syedahmershah
  • HackerNoonu/syedahmershah
  • CLCoderLegionuser/syedahmershah

Reviews & listings

  • Google Knowledge PanelSyed Ahmer Shah
  • Google Business Profileg.page
  • ClClutch
  • TpTrustpilot
  • DRDesignRush
  • TBTechBehemoths

Social

  • YouTube@ahmershahdev
  • Instagram@ahmershahdev
  • TikTok@ahmershahdev
  • Facebookahmershahdev
  • X@ahmershahdev
#ai#webdevelopment#cybersecurity#hacking
ShareXLinkedInRedditWhatsApp

← Older

How 1 Missing Line of Code Cost Anthropic $340 Billion

Newer →

Build Your Own "Private Copilot" in 10 Minutes: Ollama, Continue, and DeepSeek-V3

On this page

  • The Foundation of Blind Trust
  • The "ClawJacked" Vulnerability (CVE-2026–25253)
  • Speed Kills: The 100-Millisecond Heist
  • The 2026 Reality Check

Up next

Keep reading.

All 44 articles→
  1. 01

    How 1 Missing Line of Code Cost Anthropic $340 Billion

    Inside the 2026 Anthropic leak: A missing .npmignore line exposed 512k lines of Claude source code. Read the technical breakdown of the $340B blunder.

    Apr 3, 20269 minFirst on DEV

  2. 02

    I Tested and Compared the 6 Best AI Wireframe Generators With UI and Code Export

    I tested 6 AI wireframe generators for UI design, prototyping, and code export to compare their features, pricing, strengths, and best use cases.

    Aug 21, 20269 minAI vs RealityFirst on Medium

  3. 03

    Change One Number. Take Everything.

    IDOR affects 94% of apps. Learn how changing one URL number exposes millions of records & how to build bulletproof defenses. | Syed Ahmer Shah

    Aug 11, 20269 minThe Engineering LogsFirst on Hashnode

Available for new work · --:--:-- PKT

Have an idea?

support@ahmershah.dev
Book a call WhatsApp +92 370 4831994

On this site

  • 01About
  • 02Education
  • 03Certificates
  • 04Skills
  • 05Projects
  • 06Services
  • 07Testimonials
  • 08Contact

Pages

  • Blog
  • Saved articles
  • RSS
  • Privacy Policy
  • Terms of Service
  • llms.txt

Elsewhere · official profiles

26 links

Professional

Work history, code and credentials.

  • in/syedahmershah
  • company/syedahmershah
  • @ahmershahdev
  • syed-ahmer-shah
  • syed-ahmer-shah
  • u/syedahmershah
  • @syedahmershah
  • AWS@syedahmershah

Coding & credentials

Problem solving, verified badges.

  • u/syedahmershah
  • syedahmershah
  • users/syedahmershah
  • learner/syedahmershah

Google & business

The official listings.

  • Google Business Profileg.page
  • Syed Ahmer Shah
  • syedahmershah
  • Beaconssyedahmershah
  • syedahmershah

Social (@ahmershahdev)

Build logs, clips, threads.

  • @ahmershahdev
  • @ahmershahdev
  • @ahmershahdev
  • ahmershahdev
  • @ahmershahdev
  • @bluesky.ahmershah.dev
  • ahmershahdev

Design

Interfaces and visuals.

  • syedahmershah
  • syedahmershah

Direct

  • support@ahmershah.dev

    Support & projects

  • syedahmershahofficial@gmail.com

    Personal

  • +92 370 4831994

    Phone · WhatsApp

  • Hyderabad, Sindh, Pakistan

    Remote-first · Asia/Karachi (UTC+5)

Résumé ↗
SYED AHMER SHAH

© 2026 Syed Ahmer Shah. All rights reserved.

PrivacyTermsRSS